British intelligence have uncovered an Iranian spyware campaign stealing sensitive data from targets around the world.
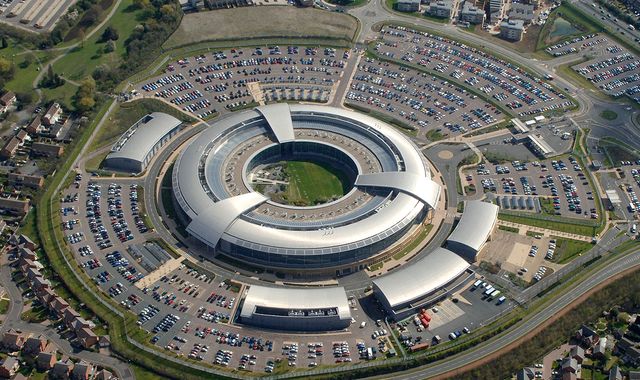
Dissidents, activists and journalists were among those targeted, GCHQ's National Cyber Security Centre (NCSC) said.
Iranian "cyber actors" reportedly used spyware to collect information such as screen captures and messaging history.
Spies in the UK discovered the plot alongside allies in the US and Netherlands.
NCSC said they had watched Iranian state hackers trying to trick targets into downloading software that can track their movements.
The cyber criminals also impersonated contacts on services like WhatsApp, built rapport and then used spyware called 'CHOSEN BRICK' to steal sensitive information.
The spyware allows attackers to steal information on a target's contacts, such as emails and social media messages, NCSC said.
It can also allow them to capture screen content and access a device's microphone.
Attackers often tailored their approach to individual targets. In some cases, it said, they used fake documents, including fabricated MRI test results, to persuade victims to download the malware, the NCSC said.
The agency said it was issuing new advice to those at risk.
Iran's embassy in London did not immediately respond to a request for comment.
The FBI, in its own advisory, said Iran's Ministry of Intelligence and Security (MOIS) was using the malware to "collect intelligence, conduct data leaks, and inflict reputational harm against their intended targets."
The US agency did not immediately respond to a request for additional details on how many people have been targeted with the malware, or where they are located.
Tehran "almost certainly" uses cyber operations to help suppress people it sees as threats, the NCSC, the FBI and the Netherlands' AIVD intelligence service, said.
The FBI's advisory said it was an update to a March 2026 warning describing alleged MOIS efforts to use the malware to collect data on targets, which was then posted online by a hacking persona known as "Handala Hack".
Handala has targeted multiple US companies and people since the start of the Iran war, including a destructive
cyberattack against Michigan-based medical supplies and services supplier Stryker in March, and the leak of FBI Director Kash Patel's personal emails later that month.
(c) Sky News 2026: British spies uncover Iranian cyber attacks targeting dissidents around the world
 Meghan shares Harry birthday post - as children moved to new school over 'security concerns'
 Raheem Sterling admits dangerous driving over Lamborghini crash
 Two dead and four seriously hurt after truck collides with pedestrians and vehicles
 Ed Sheeran responds following row surrounding Macklemore's departure from tour
 Babies killed by Lucy Letby could have been saved, inquiry finds, as cot cameras to be fitted in wards